WordPress API integration connects content or website workflows with approved external systems. It can involve the WordPress REST API, custom endpoints or outbound requests to a provider. The service is useful when content must be shared, enquiries sent to another system or administrative work synchronized. Authentication, data mapping and error handling are central parts of the implementation.
Vashu Tech services
WordPress API Integration
WordPress API integration connects content or website workflows with approved external systems. It can involve the WordPress REST API, custom endpoints or outbound requests to a provider. The service is useful when content must be shared, enquiries sent to another system or administrative work synchronized. Authentication, data mapping and error handling are central parts of the implementation.
Scope-ledYour requirements first
Clear estimatesBased on agreed work
Review pointsDefine acceptance checks
02
Understanding WordPress API Integration
WordPress can provide editable pages and articles alongside extensions for more specialized requirements. The theme, plugins, hosting and update process all influence the finished website. A project may involve a new installation, a visual redesign, a builder layout or investigation of an existing problem. These are different scopes. Review licences, editor responsibilities and compatibility before selecting tools. Existing content and user records should be protected during changes, and backups should have a tested recovery path rather than being treated as an installation checkbox.
03
Problems this work addresses
Exposing a convenient endpoint without permission checks can reveal private records, while repeated requests may create duplicate actions.
04
Work stages and practical deliverables
These stages describe the discussion scope for this service. The proposal should identify which outputs are included, the information required from you and any work that belongs to a separate agreement. Review points should make it possible to check the result against the original requirement.
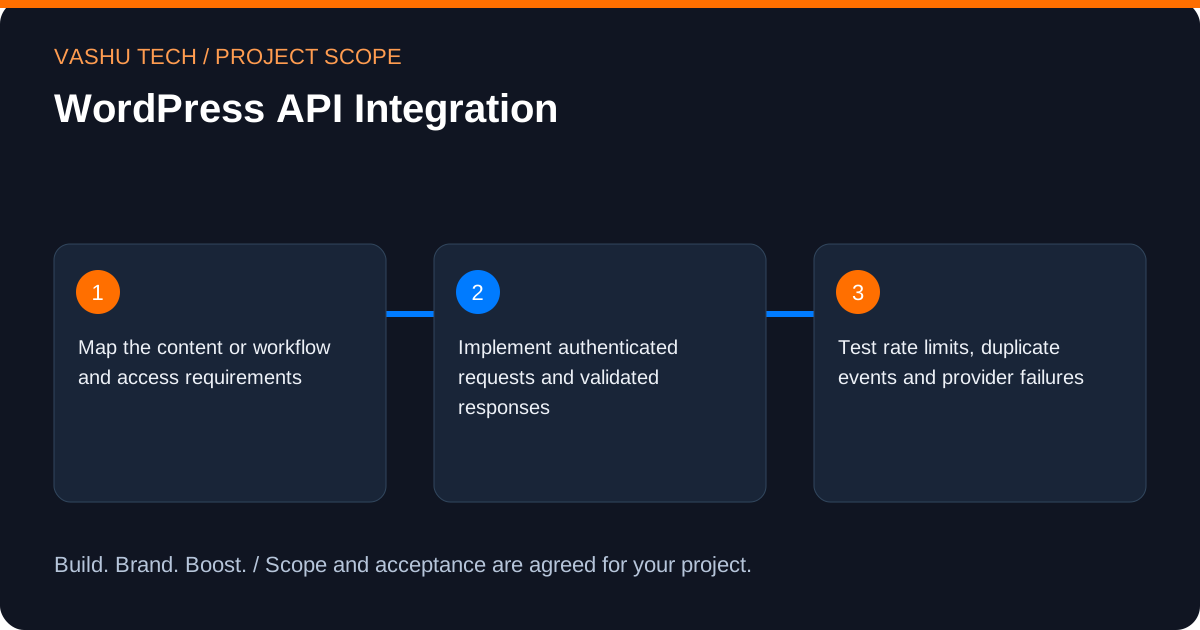
- Map the content or workflow and access requirements.
- Implement authenticated requests and validated responses.
- Test rate limits, duplicate events and provider failures.
05
Technical considerations and boundaries
API endpoints need appropriate authorization and minimal data exposure. Provider tokens must remain on the server where required. WordPress nonces are not a substitute for every form of external API authentication.
06
Business value and acceptance
The practical value is addressing this specific difficulty: exposing a convenient endpoint without permission checks can reveal private records, while repeated requests may create duplicate actions. A useful result makes the relevant journey or operational responsibility clearer. Define the acceptance checks around test rate limits, duplicate events and provider failures, and distinguish an implemented improvement from an unverified business outcome.
07
Pricing, timing and handover
An estimate depends on the existing environment, the amount of content or data involved and the agreed testing and access requirements. External licences, hosting and vendor subscriptions should be identified separately. Share any deadline and its dependencies so that feasibility can be assessed; this page does not promise a fixed price or delivery date.
08
Discuss your wordpress api integration requirements
Describe the current situation and the change you need. A public website link and a short explanation are enough to begin; arrange sensitive access separately. Request a scoped quote or contact Vashu Tech to discuss the next step.
09
Plan your WordPress API Integration scope
Start with how your team will edit the website. Choose the necessary page types, content fields and integrations before selecting a theme or plugins. For an existing installation, the current editor, licences and compatibility constraints are part of the brief; a visual change should not unnecessarily disrupt a working publishing process.
For WordPress API Integration, start by identifying the decision or workflow you want to improve. Exposing a convenient endpoint without permission checks can reveal private records, while repeated requests may create duplicate actions. Select the tasks that address that requirement; the full category of work does not have to be included in every project.
Useful starting information includes the public website, current theme or builder, relevant plugin names, editing needs and an explanation of the affected page or feature. Public links and redacted examples are enough for an initial discussion. Account access can be arranged separately after the required permissions are understood.
10
A practical WordPress API Integration planning example
Consider a business that updates services regularly but struggles to keep page layouts consistent. An agreed set of editable sections could make those updates easier while retaining approved brand choices. A plugin conflict or one broken form may instead call for a focused investigation.
Translate that example into a small, testable brief for WordPress API Integration: begin with map the content or workflow and access requirements, identify the inputs needed to implement authenticated requests and validated responses, and agree how to test rate limits, duplicate events and provider failures. This is an illustrative planning scenario, not a client case study or a promised result.
11
Review and acceptance for WordPress API Integration
Check both the public page and the editor workflow. Review forms, media, navigation and any agreed store features with representative content. Confirm that changes remain compatible with the relevant theme and plugins; update testing and licence responsibilities should be recorded separately.
Keep a short acceptance checklist alongside the proposal. For this scope, the review should include: Map the content or workflow and access requirements; Implement authenticated requests and validated responses; Test rate limits, duplicate events and provider failures. Record what was checked, which items remain open and who can approve the result. An implemented change and a business outcome are different things; neither enquiries nor sales should be assumed from a technical demonstration.
12
Handover and ongoing decisions for WordPress API Integration
The handover can explain the editing workflow, theme and plugin responsibilities, licence ownership and the included maintenance arrangements. Agree who will approve updates and how future issues should be reported.
Before handover, agree who owns the accounts, approves public information and handles future changes. Any maintenance, additional content, third-party subscription or ongoing campaign management should be listed explicitly in the proposal. Share an essential deadline early so dependencies can be discussed before a delivery schedule is agreed.
13
Planning the right fit
Audience, scope and coordination for WordPress API Integration.
Who this is for
Businesses evaluating WordPress API Integration for a new requirement or an existing website. Exposing a convenient endpoint without permission checks can reveal private records, while repeated requests may create duplicate actions.
Scope and deliverables
Map the content or workflow and access requirements Implement authenticated requests and validated responses Test rate limits, duplicate events and provider failures Scope, exclusions and acceptance evidence are agreed in the proposal.
14
Questions about WordPress API Integration
Answers to help you plan the scope and next steps.
Can the WordPress REST API expose private content?
Only if the endpoint and permissions allow it. An integration must explicitly protect private records rather than relying on an obscure URL.
What should I share for a WordPress API Integration enquiry?
Include the affected website or proposed project, the audience and the outcome you need. For this work, useful discussion points include map the content or workflow and access requirements, implement authenticated requests and validated responses, test rate limits, duplicate events and provider failures. Do not send passwords in the public form.
What affects the cost and timing of WordPress API Integration?
The amount of existing work to inspect, the agreed deliverables, access readiness and testing requirements affect the estimate. API endpoints need appropriate authorization and minimal data exposure. Provider tokens must remain on the server where required. WordPress nonces are not a substitute for every form of external API authentication. Ask for a scoped proposal rather than assuming a fixed package or completion date.
How is WordPress API Integration work checked?
Acceptance should reflect the actual requirement: map the content or workflow and access requirements; implement authenticated requests and validated responses; test rate limits, duplicate events and provider failures. Check representative content and failure cases as well as the expected successful result. Agree the evidence and handover responsibilities before work begins.
What information helps scope WordPress API Integration?
Bring the public website, current theme or builder, relevant plugin names, editing needs and an explanation of the affected page or feature. Identify your priority and which tasks you need: Map the content or workflow and access requirements; Implement authenticated requests and validated responses; Test rate limits, duplicate events and provider failures. Share public or redacted information first; arrange sensitive access separately.
What should be agreed at the handover for WordPress API Integration?
The handover can explain the editing workflow, theme and plugin responsibilities, licence ownership and the included maintenance arrangements. Agree who will approve updates and how future issues should be reported. Confirm account ownership, approval responsibilities and any ongoing support separately from the initial work.
Discuss your requirements
Plan your WordPress API Integration project
Share your starting point and priorities. We can discuss the scope, required information and acceptance checks before providing an estimate.
Tell us about your project.
Send your requirements to our team. Please leave out passwords and confidential access details.