Discuss Website Security and Bug Fixing around the actual users, content and workflow, with a proposal that states the selected tasks and acceptance evidence.
Vashu Tech services
Website Security and Bug Fixing
Discuss Website Security and Bug Fixing around the actual users, content and workflow, with a proposal that states the selected tasks and acceptance evidence.
Scope-ledYour requirements first
Clear estimatesBased on agreed work
Review pointsDefine acceptance checks
02
Define the requirement
03
Scope to agree
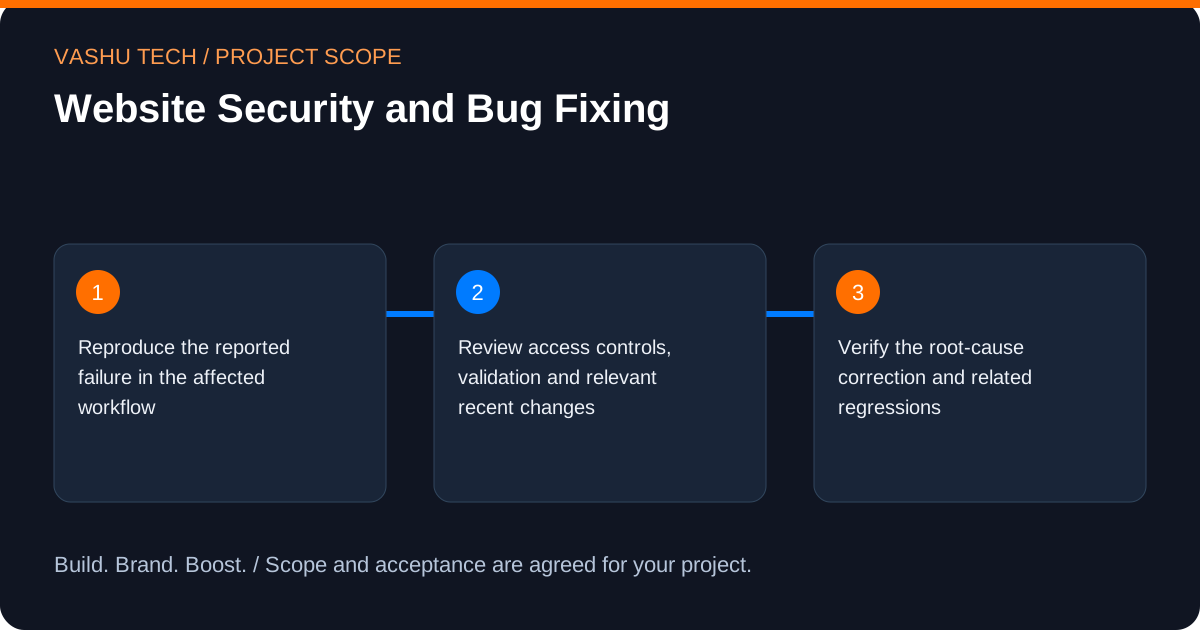
- Reproduce the reported failure in the affected workflow
- Review access controls, validation and relevant recent changes
- Verify the root-cause correction and related regressions
04
Project discussion
Share the existing site, users and intended outcome. Agree permissions, preservation of existing records, testing and ongoing ownership. Request a scoped proposal.
05
When this work is useful
A reported error or suspected security problem needs careful reproduction and evidence. A broken form, permission defect and possible compromise require different investigations. Preserve existing records and relevant diagnostic information before making changes that could obscure the cause.
06
Technical considerations and working process
Agree safe access and the affected workflow. Review validation, permissions and recent changes where relevant. For suspected compromise, discuss containment and recovery separately from a cosmetic repair. Verify the correction and related regression paths. No website can be promised permanently secure, and a successful fix is not proof that every unrelated risk has been assessed.
The working process is to inspect the starting point, agree the selected tasks, implement the change and verify the result. For Website Security and Bug Fixing, this includes reproduce the reported failure in the affected workflow; review access controls, validation and relevant recent changes; verify the root-cause correction and related regressions. Record access dependencies and who approves the final work.
07
Cost, timing and support
The estimate depends on existing work to inspect, content and data volume, integrations and the agreed testing. Hosting, licences and provider subscriptions are identified separately. Share any deadline and the reason for it so feasibility can be assessed. No fixed price, completion date or business result is promised. Clarify maintenance and handover responsibilities before release.
08
Plan your Website Security and Bug Fixing scope
A useful website brief connects page design to visitor decisions. Identify what someone needs to understand before making contact, then decide how navigation, copy, visual hierarchy and forms should support that journey. Keep essential company information easy to find on a phone as well as a larger screen.
For Website Security and Bug Fixing, start by identifying the decision or workflow you want to improve. Separate the essential work from later enhancements so the initial proposal has a clear purpose. Select the tasks that address that requirement; the full category of work does not have to be included in every project.
Useful starting information includes your current public website, approved brand materials, a draft page list, available copy and the enquiry destination. Public links and redacted examples are enough for an initial discussion. Account access can be arranged separately after the required permissions are understood.
09
A practical Website Security and Bug Fixing planning example
Consider a service business whose offer is spread across several pages. A practical brief could make the service differences easier to compare, give each page a clear next step and check whether a visitor can complete an enquiry without losing entered information.
Translate that example into a small, testable brief for Website Security and Bug Fixing: begin with map the page structure and visitor actions, identify the inputs needed to design and implement the agreed responsive journeys, and agree how to review content, navigation and enquiry behaviour. This is an illustrative planning scenario, not a client case study or a promised result.
10
Review and acceptance for Website Security and Bug Fixing
Review representative pages at phone, tablet and desktop widths. Try keyboard navigation, long headings, missing images and invalid form input, alongside a successful submission. Where URLs change, review the redirect mapping and retained public information rather than judging the work by screenshots alone.
Keep a short acceptance checklist alongside the proposal. For this scope, the review should include: Map the page structure and visitor actions; Design and implement the agreed responsive journeys; Review content, navigation and enquiry behaviour. Record what was checked, which items remain open and who can approve the result. An implemented change and a business outcome are different things; neither enquiries nor sales should be assumed from a technical demonstration.
11
Handover and ongoing decisions for Website Security and Bug Fixing
The handover can identify the reusable layouts, editable content areas and the approved contact routes. Agree which source files or implementation notes are included and who will maintain hosting, content and future page changes.
Before handover, agree who owns the accounts, approves public information and handles future changes. Any maintenance, additional content, third-party subscription or ongoing campaign management should be listed explicitly in the proposal. Share an essential deadline early so dependencies can be discussed before a delivery schedule is agreed.
12
Planning the right fit
Audience, scope and coordination for Website Security and Bug Fixing.
Scope and deliverables
Reproduce the reported failure in the affected workflow Review access controls, validation and relevant recent changes Verify the root-cause correction and related regressions
13
Questions about Website Security and Bug Fixing
Answers to help you plan the scope and next steps.
What should I send with a bug report?
Describe the expected behaviour, what actually happens, the affected URL and any relevant device or recent change. Share screenshots without private records or passwords; arrange sensitive access through a separate channel.
What should I share for Website Security and Bug Fixing?
Explain the current situation, intended users and the problem to solve. Relevant discussion points include reproduce the reported failure in the affected workflow; review access controls, validation and relevant recent changes; verify the root-cause correction and related regressions. Do not submit passwords in the enquiry form.
What affects the estimate for Website Security and Bug Fixing?
Existing implementation complexity, records to preserve, access readiness and the agreed scope affect the estimate. Agree safe access and the affected workflow. Review validation, permissions and recent changes where relevant. For suspected compromise, discuss containment and recovery separately from a cosmetic repair. Verify the correction and related regression paths. No website can be promised permanently secure, and a successful fix is not proof that every unrelated risk has been assessed.
How is Website Security and Bug Fixing checked?
Agree representative journeys and acceptance evidence around these tasks: reproduce the reported failure in the affected workflow; review access controls, validation and relevant recent changes; verify the root-cause correction and related regressions. Verify failure cases and handover responsibilities as well as the intended result.
What information helps scope Website Security and Bug Fixing?
Bring your current public website, approved brand materials, a draft page list, available copy and the enquiry destination. Identify your priority and which tasks you need: Map the page structure and visitor actions; Design and implement the agreed responsive journeys; Review content, navigation and enquiry behaviour. Share public or redacted information first; arrange sensitive access separately.
What should be agreed at the handover for Website Security and Bug Fixing?
The handover can identify the reusable layouts, editable content areas and the approved contact routes. Agree which source files or implementation notes are included and who will maintain hosting, content and future page changes. Confirm account ownership, approval responsibilities and any ongoing support separately from the initial work.
Discuss your requirements
Plan your Website Security and Bug Fixing project
Share your starting point and priorities. We can discuss the scope, required information and acceptance checks before providing an estimate.
Tell us about your project.
Send your requirements to our team. Please leave out passwords and confidential access details.